FedRAMP Compliance | A-LIGN
  • Services
        • SOC Assessments 

        • SOC 1
        • SOC 2
        • ISO Certifications 

        • ISO 27001
        • ISO 27701
        • ISO 22301
        • ISO 42001
        • ISO 45001 
        • ISO 14001
        • ISO 9001
        • Federal Assessments 

        • All Government
        • FedRAMP
        • GovRAMP
        • FISMA
        • CMMC
        • NIST 800-171
        • Healthcare Assessments 

        • All Healthcare
        • HITRUST
        • HIPAA
        • Cybersecurity 

        • Penetration testing
        • Red team services
        • Ransomware preparedness assessment
        • Social engineering
        • Vulnerability assessment service
        • Privacy 

        • GDPR
        • CCPA/CPRA
        • PCI Assessments 

        • PCI DSS
        • PCI SSF
        • Additional Services 

        • International Services
        • Multi-Framework
        • AI Governance
        • AS9100
        • Microsoft SSPA
        • NIS2
        • C5
        • SOX 404
        • CSA STAR
        • Business Continuity & Disaster Recovery
        • Limited Access Death Master File
        • All Services
  • Platform
  • Company
        • About Us
        • Partners
        • Meet our team
        • Board of Directors
        • Careers
        • Community
        • image

          Veteran-owned elite cybersecurity team expands A-LIGN’s ability to help organizations move beyond compliance and stay…

          Learn more
  • Customers
  • Resources
        • Quick links

        • Resource Center
        • Blogs
        • Case Studies 
        • Videos
        • Events
        • By service

        • SOC 2 
        • ISO 27001 
        • ISO 42001 
        • CMMC
        • FedRAMP
        • HITRUST 
        • PenTest
        • Featured Resources

          image
          image
          image
          image
  • A-SCEND Login
  • Careers
CONTACT US
FedRAMP assessment by A-LIGN

Unlock federal business with FedRAMP

A-LIGN is a FedRAMP independent assessor with a FedRAMP 20x certified audit platform. FedRAMP demands specialized expertise that few firms can deliver, and A-LIGN brings deep federal experience to every engagement so you reach certification with confidence.

Talk to an expert
FedRAMP assessor

Top 3

federal clients served

250+

client satisfaction rating

96%

federal assessments completed

1k+

WHy A-lign

FedRAMP 20x with a top federal assessor

Unlock federal revenue that used to require years of upfront investment with FedRAMP 20x. Engagements run on transparent milestones managed through A-SCEND, A-LIGN's own FedRAMP 20x–certified audit platform. 

Get started
Illustration of A-SCEND mapping shared audit evidence across SOC 2, SOC 1, ISO 27001, and HIPAA

A new path to certification

FedRAMP authorization used to mean years of runway and seven-figure investment before you earned your first federal dollar. Not anymore. With 20x, A-LIGN gets you to certification in weeks, not months, at a fraction of the cost – on a path sized for your team, your timeline, and your budget.

Federal revenue, now within reach

Whether you're moving from Rev 5 or starting fresh with a Class A certification, A-LIGN is your partner on the path to federal revenue. We'll connect you with the right readiness provider from our trusted network, and stay independent as your assessor – so you're prepared, and your certification makes federal revenue within reach.

Transparent execution

Clear milestones and project plans keep you informed from kickoff to certification: no surprises, no missed dependencies. It's a process refined through our experience as a Top 3 FedRAMP assessor (3PAO), so you always know what's coming and what's needed next.

Efficient audit management with A-SCEND

A-LIGN's audit management platform, A-SCEND, is itself FedRAMP 20x certified. That means your assessment runs on technology that has been through the exact process you're navigating – we don't just assess the standard, we've met it.

Why A-LIGN

Leverage a top 3 3PAO to win federal business

Few assessors have seen more paths to certification than A-LIGN. As a Top 3 3PAO, we've guided organizations through every route – pursuing 20x, transitioning from Rev 5, or maintaining an existing certification – and we know the route to get you there.

Contact us

Readiness Assessment

Know where you stand. With a readiness assessment, the A-LIGN team reviews your environment against the desired FedRAMP certification level so that you begin with a clear picture of the path ahead.

FedRAMP Certification

As a top 3PAO, we conduct an independent assessment to help you achieve FedRAMP Certification across all certification classes as they become available.

Annual Assessment

Certification isn’t a one-time event. We combine annual assessments with continuous monitoring to keep your certification current between cycles. No lapses in compliance, no scrambling.

FedRAMP 20x Transition

Certified under Rev 5? We’ll guide your transition assessment to FedRAMP 20x before the Rev 5 path sunsets on your timeline, not the deadline’s.

Rev 5 Authorization

Achieve or maintain Rev 5 Authorization with a fully established 3PAO. A-LIGN’s extensive federal expertise guides your assessment under NIST 800-53 Revision 5 from start to finish.

A-LIGN by the numbers

audits completed
36k+
customer satisfaction
96%
clients globally
6.4k+
auditors globally
400+
Platform Innovation

Modernized compliance makes rigor repeatable

A-SCEND pairs expert auditors and powerful technology with a process sharpened over 36,000+ audits. The result: compliance that helps you grow and expand into new markets with rigor built in, not bolted on.

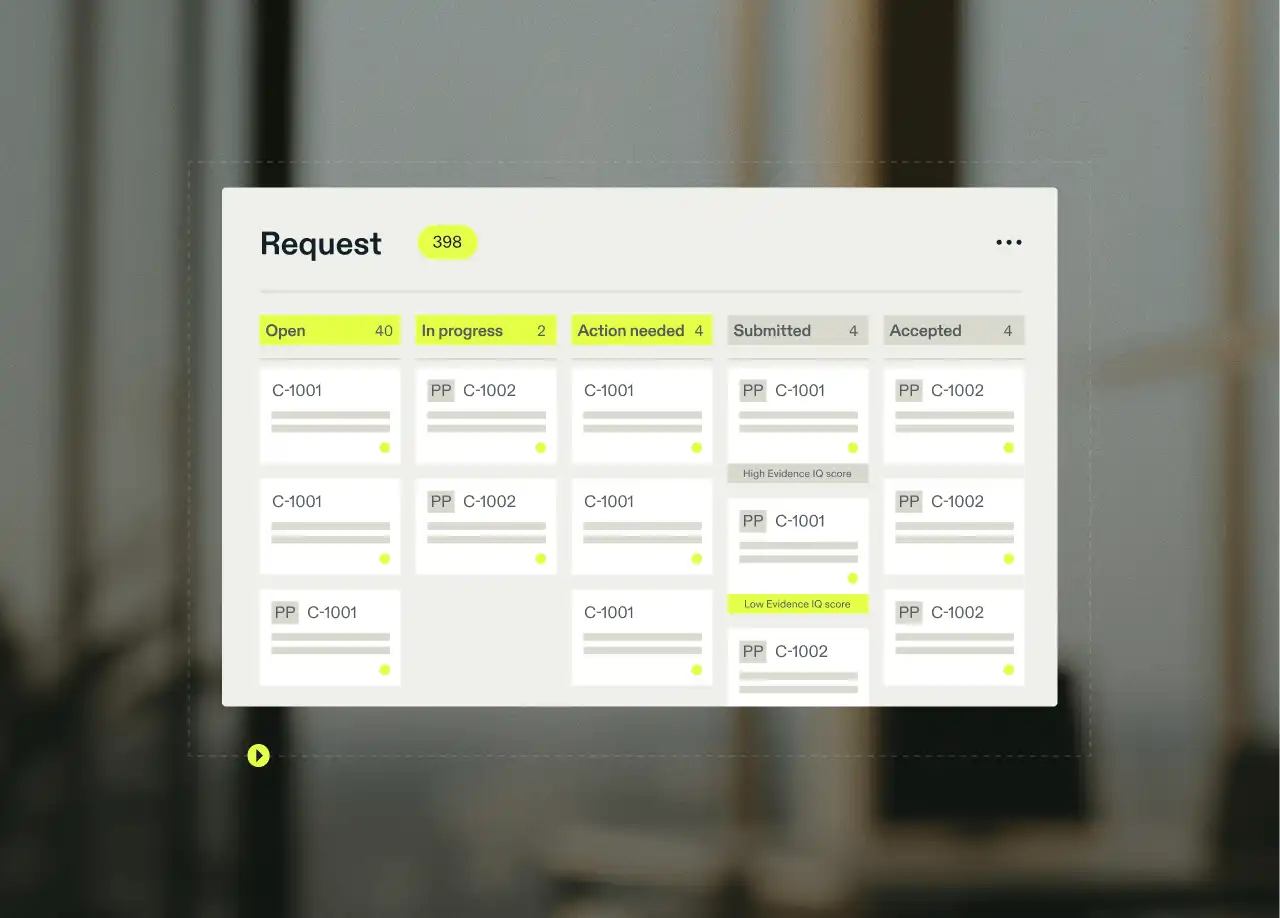
A-SCEND platform showing centralized audit requests
A-SCEND platform showing the guided audit workflow stages
EFFICIENT AUDIT PLATFORM

Tech-Enabled Audit Management

A-SCEND is an end-to-end audit management platform built from real-world audit practice. By eliminating repetitive tasks, delivering real-time visibility and control, and enforcing consistency and precision across every engagement, A-SCEND elevates audit quality without sacrificing rigor.

Purpose-built technology enforces consistency, strengthens audit quality, and drives efficiency, every cycle, every framework, every year.

RIGOROUS METHODOLOGY 

Precision at Every Stage

Every A-SCEND engagement follows a disciplined methodology built to withstand scrutiny.

That rigor carries through every stage of our audit process, from precise scoping and a deep understanding of your business up front, with executive oversight and built-in quality checks, to expert review and fine-tuning for a polished, high-quality report.

That experience and discipline bring greater certainty and help prevent the leading causes of report rejection: incomplete scope and missing controls.

SUCCESS STORIES

Trusted across the federal compliance landscape

From FedRAMP 20x to multi-framework programs, see why federal cloud providers choose A-LIGN as their 3PAO.

“What sets A-LIGN apart is that they’re not just guiding us through FedRAMP 20x — they’re in it for the long haul with us. Their team understands the challenges firsthand, and that partnership has been invaluable as we worked toward authorization.”

Learn more

Founder

Ozzie Saeed

IntelliGRC

Intelligrc logo

“We chose A-LIGN as our auditor because of their deep experience and recognized expertise in FedRAMP, StateRAMP, ISO and SOC, offering end-to-end support for our compliance efforts. A-LIGN has responsive and knowledgeable teams which ensures quick resolution of queries or challenges during the audit process as well as ongoing support beyond the audit.”

Read case study

Director of GRC

Nicole Anderson

Anthology

Anthology logo

“RegScale operates in highly regulated environments where trust and compliance are non-negotiable. That’s why we chose A-LIGN — experts with deep federal compliance expertise across the full spectrum of frameworks — to serve as our trusted audit partner. A-LIGN’s reputation for delivering high-quality, timely results solidified them as the trusted audit provider we were looking for to elevate our compliance program and achieve our federal compliance goals.”

Learn more

CISO

Dale Hoak

RegScale

RegScale logo

“A-LIGN has been an asset as we navigated FedRAMP, PCI, and SOC 2 compliance. They have helped guide us through the process. A-LIGN has greatly contributed to our success. The various people we’ve worked have been incredibly knowledgeable and capable.”

Security and Risk Management Executive

Global Business Services Organization

Helpful Resources

Support for your compliance journey

From guides to whitepapers, we've got the resources to move your compliance program forward.

View resources
resource checklist FedRAMP 20x 6 0
CHECKLIST
FedRAMP 20x Compliance Checklist
Learn more
CASE STUDY
IntelliGRC earns FedRAMP 20x Low authorization
Learn more
VIDEO
The Evolution of FedRAMP: Exploring 20X w/ Matt Earley
Watch now
BLOG
FedRAMP 20x: What It Is, How It Differs from Rev. 5, and Where It Stands Today
Learn more

Frequently asked questions

Contact us

What is FedRAMP, and does my organization need it?

FedRAMP, the Federal Risk and Authorization Management Program, is a U.S. government-wide framework that standardizes security assessment, authorization, and continuous monitoring for cloud services used by federal agencies. If your organization provides a cloud service (SaaS, PaaS, or IaaS) to any U.S. federal agency and that service handles federal data, FedRAMP certificationis either required or strongly expected. The program allows CSPs to conduct business with the federal government.

What is the difference between FedRAMP Rev 5 and FedRAMP 20x?

Rev 5 is the traditional authorization pathway based on the full NIST SP 800-53 Revision 5 control catalog. It is comprehensive, applicable to all impact levels, and required for most existing agency relationships. FedRAMP 20x is a modernized pathway that uses automated control validation and continuous monitoring to streamline the assessment process, particularly for Low and Moderate impact systems. 20x significantly reduces time-to-authorization and cost for eligible systems. A-LIGN supports both pathways and can advise which is appropriate given your system architecture and target agency.

How much does a FedRAMP assessment cost?

FedRAMP assessment costs vary significantly based on class level, system complexity, number of controls in scope, and whether penetration testing is included. A-LIGN provides transparent milestone-based pricing, so contact the team for a scoped estimate based on your specific system boundaries.

How long does FedRAMP certification take?

A full Rev 5 authorization typically takes 12 to 18 months from initial kickoff to an agency-issued ATO, assuming the CSP's documentation is in reasonable shape at the start. Readiness gaps, incomplete SSP documentation, or slow agency review cycles are the most common causes of delay. FedRAMP 20x Class A certifications can be completed in weeks for well-prepared systems. A-LIGN's A-SCEND platform gives you real-time visibility into exactly where you are in the process and what is needed next.

Do we need an agency sponsor for FedRAMP?

Under the traditional Rev 5 agency authorization path, yes, a federal agency must agree to sponsor your organization. However, FedRAMP 20x does not require agency sponsorship, making entry more accessible. A-LIGN will advise you on the right sponsorship path based on your existing and targeted agency relationships.

Is a penetration test required for FedRAMP?

Rev 5: yes. Penetration testing is a baseline control in every class, runs at least every 12 months, and Classes C and D also require red team exercises. 20x: There is no formal rule or Key Security Indicator mandates a pen test, but it is one of the named techniques for meeting the vulnerability detection rules that become mandatory December 7, 2026.

Ready to get started?

Contact us

A-LIGN is the leading cybersecurity compliance partner, trusted by over 6,400 organizations worldwide to navigate the complexities of compliance, audit, and risk. With a tech-enabled delivery model and deep domain expertise, A-LIGN delivers high-quality, efficient audits across frameworks including SOC 2, ISO 27001, FedRAMP, CMMC, ISO 42001, PCI, and HITRUST.

CONTACT US
  • Services
  • SOC 1
  • SOC 2
  • ISO 27001
  • ISO 42001
  • CMMC
  • HITRUST
  • FedRAMP
  • Penetration Testing
  • PCI DSS
  • HIPAA
  • International Services
  • Multi-Framework
  • AI Governance
  • All Services
  • Company 
  • About us
  • Partners
  • Platform
  • Careers
  • Our Team
  • Community
  • Trust Center
  • Contact Us
  • Customers 
  • Customer Stories 
  • Resources
  • Resource Center
  • Blogs
  • Case Studies
  • Videos
  • Events
  • Newsletter Sign-up
  • Guides
  • SOC 2 Compliance
  • ISO 27001 Certification
  • CMMC Compliance
  • ISO 42001 Compliance
  • HITRUST Certification
  • ISO Certificate Directory
  • Privacy Policy
  • Cookie Policy
  • Impartiality and Inquiries
  • Acceptable Use Policy
  • Sitemap
  • AI Information

Price and Associates CPAs, LLC dba A-LIGN ASSURANCE is a licensed certified public accounting firm registered with the Public Company Accounting Oversight Board (PCAOB). A-LIGN Compliance and Security, Inc. dba A-LIGN is a leading cybersecurity and compliance professional services firm.

A-LIGN 2026. All rights reserved.

  • Services
    • SOC Assessments
      • SOC 1
      • SOC 2
    • ISO Certifications 
      • ISO 27001
      • ISO 27701
      • ISO 22301
      • ISO 42001
      • ISO 45001 
      • ISO 14001
      • ISO 9001
    • Healthcare Assessments 
      • All Healthcare
      • HITRUST
      • HIPAA
    • Federal Assessments
      • All Government
      • FedRAMP
      • StateRAMP
      • FISMA
      • CMMC
      • NIST 800-171
    • PCI Assessments
      • PCI DSS
      • PCI SSF
    • Cybersecurity
      • Penetration testing
      • Red team services
      • Ransomware preparedness assessment
      • Social engineering
      • Vulnerability assessment service
    • Privacy
      • GDPR
      • CCPA/CPRA
    • Additional Services
      • International Services 
      • Multi-Framework 
      • AS9100
      • Microsoft SSPA
      • NIS2
      • C5
      • SOX 404
      • CSA STAR
      • Business Continuity & Disaster Recovery
      • Limited Access Death Master File
    • All Services
  • Platform
  • Company
    • About Us
    • Partners
    • Meet our team
    • Board of Directors
    • Careers
    • Community
  • Customers
  • Resources
    • Resource Center
    • Blogs
    • Case Studies 
    • Videos 
    • Events
    • By Service
      • SOC 2 
      • ISO 27001 
      • ISO 42001 
      • CMMC
      • FedRAMP
      • HITRUST
      • PenTest 
  • A-SCEND Login
  • Careers
CONTACT US