ISO 42001 Certification for AI Governance | A-LIGN
  • Services
        • SOC Assessments 

        • SOC 1
        • SOC 2
        • ISO Certifications 

        • ISO 27001
        • ISO 27701
        • ISO 22301
        • ISO 42001
        • ISO 45001 
        • ISO 14001
        • ISO 9001
        • Federal Assessments 

        • All Government
        • FedRAMP
        • GovRAMP
        • FISMA
        • CMMC
        • NIST 800-171
        • Healthcare Assessments 

        • All Healthcare
        • HITRUST
        • HIPAA
        • Cybersecurity 

        • Penetration testing
        • Red team services
        • Ransomware preparedness assessment
        • Social engineering
        • Vulnerability assessment service
        • Privacy 

        • GDPR
        • CCPA/CPRA
        • PCI Assessments 

        • PCI DSS
        • PCI SSF
        • Additional Services 

        • International Services
        • Multi-Framework
        • AI Governance
        • AS9100
        • Microsoft SSPA
        • NIS2
        • C5
        • SOX 404
        • CSA STAR
        • Business Continuity & Disaster Recovery
        • Limited Access Death Master File
        • All Services
  • Platform
  • Company
        • About Us
        • Partners
        • Meet our team
        • Board of Directors
        • Careers
        • Community
        • image

          With audit demands at an all-time high, A-LIGN is enabling global organizations to modernize compliance,…

          Learn more
  • Customers
  • Resources
        • Quick links

        • Resource Center
        • Blogs
        • Case Studies 
        • Videos
        • Events
        • By service

        • SOC 2 
        • ISO 27001 
        • ISO 42001 
        • CMMC
        • FedRAMP
        • HITRUST 
        • PenTest
        • Featured Resources

          image
          image
          image
          image
  • A-SCEND Login
  • Careers
CONTACT US
ISO 42001 certification by A-LIGN

ISO 42001: Don’t fall behind on AI governance

A-LIGN is an accredited ISO 42001 certification body and was among the first to certify AI management systems worldwide. Demonstrate your commitment to responsible AI and differentiate yourself from the competition with an ISO 42001 certification from A-LIGN.

Get started
client satisfaction rating

96%

years of experience

20+

ISO audits completed

5.9k+

ISO auditors globally

60+

WHy A-lign

The proven partner for ISO 42001 certification

A-LIGN was among the first accredited certification bodies for ISO 42001 and has completed nearly 6,000 ISO assessments globally. That depth means we deliver a certification that withstands scrutiny and signals credibility to customers, regulators, and partners.

Talk to an expert
Illustration of A-SCEND mapping shared audit evidence across SOC 2, SOC 1, ISO 27001, and HIPAA

Future-proofing AI governance strategy

AI regulations and expectations are evolving rapidly. ISO 42001 is centered on building responsible AI Management, establishing flexible, scalable processes that position clients to adapt as requirements mature rather than scrambling to catch up later.

Increase customer trust and confidence

As AI becomes more embedded in business operations, stakeholders are demanding greater transparency, accountability, and formalized security structures. ISO 42001 provides a recognized, third-party validated signal that AI systems are being continuously managed and improved.

Outpace competitors still drafting their AI compliance program

The proliferation of AI technology across industries and geographies is changing how organizations will compete. ISO 42001 sets clients apart from competitors who are still figuring out their AI governance story. Certification provides a concrete, credible differentiator and first-mover advantage that can influence purchasing decisions and partnerships.

OUR SERVICES

ISO 42001 services to meet your needs

The ISO 42001 framework enables organizations to manage risks and demonstrate ethical and responsible AI usage across the AI systems lifecycle. The framework validates that an organization’s AI Management System (AIMS) is successfully implemented, monitored, and performing as intended.

Contact us

Pre-Assessment

The ISO 42001 readiness assessment enables organizations to prepare all materials and processes for audit and identify areas of improvement before the formal assessment.

ISO 42001 Certification

The ISO 42001 assessment validates an organization’s conformity of their AI Management System (AIMS) with the documented standards and provides assurance regarding the security of AI systems and data.

A-LIGN by the numbers

audits completed
36k+
customer satisfaction
96%
clients globally
6.4k+
auditors globally
400+
Platform Innovation

Modernized compliance makes rigor repeatable

A-SCEND combines human expertise and robust processes with powerful technology to help you achieve compliance, grow your business, and expand into new markets without sacrificing rigor.

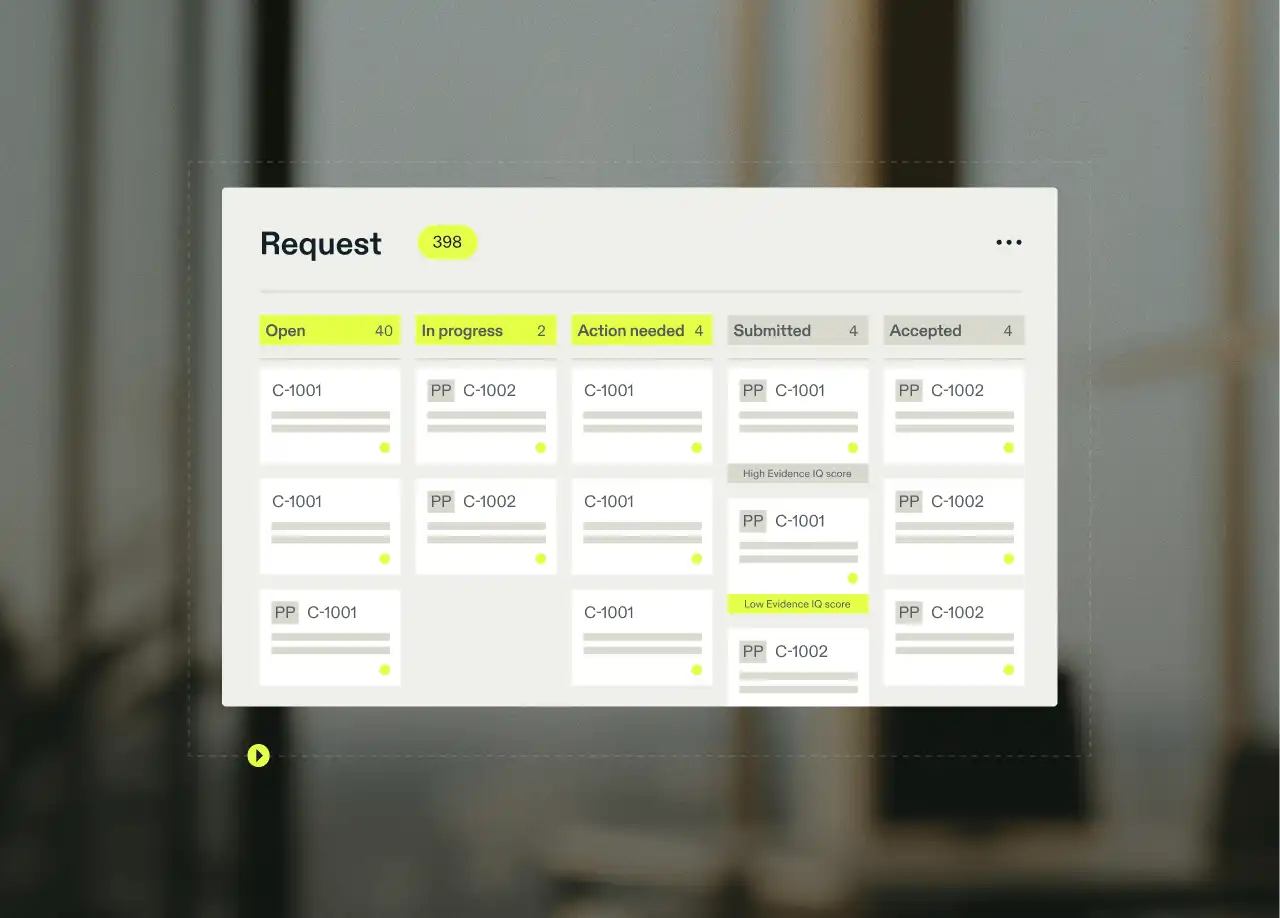
A-SCEND platform showing centralized audit requests
A-SCEND platform showing the guided audit workflow stages
EFFICIENT AUDIT PLATFORM

Tech-enabled audit management

A-SCEND is an end-to-end audit management platform built from real-world audit practice. By eliminating repetitive tasks, delivering real-time visibility and control, and enforcing consistency and precision across every engagement, A-SCEND elevates audit quality without sacrificing rigor.

Purpose-built technology enforces consistency, strengthens audit quality, and drives efficiency, every cycle, every framework, every year.

RIGOROUS METHODOLOGY 

Precision at every stage

Every A-SCEND engagement follows a disciplined methodology built to withstand scrutiny.

That rigor carries through every stage of our audit process, from precise scoping and a deep understanding of your business up front, with executive oversight and built-in quality checks, to expert review and fine-tuning for a polished, high-quality report.

That experience and discipline bring greater certainty and help prevent the leading causes of report rejection: incomplete scope and missing controls.

SUCCESS STORIES

Early movers in responsible AI choose A-LIGN

As one of the first accredited ISO 42001 assessors, A-LIGN has guided early adopters through certifying their AI management systems.

“Working with A-LIGN to achieve this certification has been a genuine step forward in how we manage and govern AI. It sets the tone for how we’ll support our clients on that same path, backed by a partner who understands the rigor required.”

Learn more

Managing Director

Paul Stevens

AvISO

Aviso logo

“A-LIGN’s deep understanding of ISO 42001 and other key regulations was instrumental in ensuring that Webdox’s AI products and CLM platform not only met compliance standards but also set a benchmark in security, ethics, and responsibility.”

Learn more

Security Officer

Nicole Barrueto

Webdox

Webdox logo

“Our goal was to leverage A-LIGN’s expertise to not only validate our approach, but to gain valuable insights from the audit process, rather than merely pursuing the certification. We sought an audit partner with a stellar reputation, and A-LIGN met all our criteria perfectly.”

Learn more

Founder and CEO

Tom McNamara

Atoro

Atoro logo

“We ultimately chose A-LIGN because their audit process was straightforward, supportive, and transparent right from the start. Unlike other providers we considered, A-LIGN made what could have been a complex and overwhelming journey feel manageable and well-structured. The team took the time to guide us through each step, ensuring we understood what was required and why.”

Knowledge Consultant

Angela Johnson

Step 5

Step 5 logo
Helpful Resources

Support for your compliance journey

From guides to whitepapers, we've got the resources to move your compliance program forward.

View resources
Blog
Understanding ISO 42001
Learn more
Webinar
The Ultimate Guide to ISO 42001
Watch now
Case study
Synthesia becomes first AI video platform to earn ISO 42001 certification
Learn more
Blog
U.S. AI Law Is Here. This Is What You Need to Know.
Learn more

Frequently asked questions

Contact us

What is ISO 42001 and why does it matter now?

ISO/IEC 42001 is the world's first international standard for AI Management Systems (AIMS), published in December 2023. It gives organizations that develop, deploy, or use AI a framework for managing AI-related risks, ensuring transparency and accountability, and addressing ethical, privacy, and safety concerns. It matters now because AI governance expectations are arriving faster than AI regulation: enterprise procurement teams and regulators are asking for evidence of responsible AI management before any law requires it, and ISO 42001 is the recognized benchmark that evidence is measured against.

What does ISO 42001 certification involve?

Achieving ISO 42001 certification involves establishing an AI Management System (AIMS) covering leadership commitment, AI risk assessment and treatment, AI impact assessments, lifecycle controls for AI systems, transparency and accountability measures, and a process for continual improvement. Certification follows the same two-stage audit structure as ISO 27001: a Stage 1 documentation review confirms the AIMS is designed correctly, and a Stage 2 audit evaluates whether it is implemented and operating effectively. Most organizations begin with a readiness assessment to identify gaps before Stage 1. Certificates are valid for three years, with annual surveillance audits in between.

Does ISO 42001 help with regulatory AI requirements like the EU AI Act?

ISO 42001 and the EU AI Act share common objectives around risk-based AI governance, transparency, and accountability, but certification does not constitute legal compliance with the EU AI Act and is not a safe harbor under it. What certification does provide is a documented governance posture – risk management processes, impact assessments, data governance, human oversight, and post-market monitoring – that maps directly onto the Act's requirements for high-risk AI systems. Organizations that establish an AIMS to ISO 42001 are better positioned to meet those requirements as enforcement progresses, and to evidence due diligence in a regulatory review. ISO 42001 also maps to the NIST AI Risk Management Framework, so a single AIMS can serve both.

How much does ISO 42001 certification cost?

ISO 42001 certification cost varies with the number and complexity of AI systems in scope, organizational size, existing governance maturity, and whether a readiness assessment and AI impact assessments are included. Contact A-LIGN for a scoping assessment specific to your AI systems and intended scope.

What is the difference between ISO 42001 and ISO 27001?

ISO 27001 is the international standard for Information Security Management Systems; it governs how an organization protects the confidentiality, integrity, and availability of information. ISO 42001 is the international standard for AI Management Systems; it governs how an organization manages AI-specific risks such as bias, transparency, human oversight, and the impact of AI decisions on individuals. The two are complementary rather than overlapping: AI systems handle data protected under ISO 27001, while the risks those systems create are addressed by ISO 42001. Both follow the same management-system structure, so organizations pursuing both can share evidence and run the audits together. A-LIGN is accredited for both standards and assesses them concurrently.

Does ISO 42001 certify individual AI models or the organization?

ISO 42001 certifies the organization's AI Management System, not any individual AI model. The certificate states that the organization's processes for developing, deploying, monitoring, and governing AI systems within the defined scope have been independently audited and conform to the standard.

How do I choose an accredited ISO 42001 certification body?

An ISO 42001 certificate carries international recognition only when the certification body is accredited by a member of the International Accreditation Forum, such as ANAB or UKAS in the United Kingdom. A certificate from an unaccredited body may not satisfy contract language or regulatory expectations that specify accredited certification. When comparing bodies, verify accreditation in the accreditation body's public registry, ask how many ISO 42001 audits the body has actually completed – the standard is new and completed-audit volume varies widely – and confirm the auditors have AI and data governance experience. A-LIGN was among the first accredited ISO 42001 certification bodies and has certified AI management systems across multiple industries.

Ready to get started?

Contact us

A-LIGN is the leading cybersecurity compliance partner, trusted by over 6,400 organizations worldwide to navigate the complexities of compliance, audit, and risk. With a tech-enabled delivery model and deep domain expertise, A-LIGN delivers high-quality, efficient audits across frameworks including SOC 2, ISO 27001, FedRAMP, CMMC, ISO 42001, PCI, and HITRUST.

CONTACT US
  • Services
  • SOC 1
  • SOC 2
  • ISO 27001
  • ISO 42001
  • CMMC
  • HITRUST
  • FedRAMP
  • Penetration Testing
  • PCI DSS
  • HIPAA
  • International Services
  • Multi-Framework
  • AI Governance
  • All Services
  • Company 
  • About us
  • Partners
  • Platform
  • Careers
  • Our Team
  • Community
  • Trust Center
  • Contact Us
  • Customers 
  • Customer Stories 
  • Resources
  • Resource Center
  • Blogs
  • Case Studies
  • Videos
  • Events
  • Newsletter Sign-up
  • Guides
  • SOC 2 Compliance
  • ISO 27001 Certification
  • CMMC Compliance
  • ISO 42001 Compliance
  • HITRUST Certification
  • ISO Certificate Directory
  • Privacy Policy
  • Cookie Policy
  • Impartiality and Inquiries
  • Acceptable Use Policy
  • Sitemap
  • AI Information

Price and Associates CPAs, LLC dba A-LIGN ASSURANCE is a licensed certified public accounting firm registered with the Public Company Accounting Oversight Board (PCAOB). A-LIGN Compliance and Security, Inc. dba A-LIGN is a leading cybersecurity and compliance professional services firm.

A-LIGN 2026. All rights reserved.

  • Services
    • SOC Assessments
      • SOC 1
      • SOC 2
    • ISO Certifications 
      • ISO 27001
      • ISO 27701
      • ISO 22301
      • ISO 42001
      • ISO 45001 
      • ISO 14001
      • ISO 9001
    • Healthcare Assessments 
      • All Healthcare
      • HITRUST
      • HIPAA
    • Federal Assessments
      • All Government
      • FedRAMP
      • StateRAMP
      • FISMA
      • CMMC
      • NIST 800-171
    • PCI Assessments
      • PCI DSS
      • PCI SSF
    • Cybersecurity
      • Penetration testing
      • Red team services
      • Ransomware preparedness assessment
      • Social engineering
      • Vulnerability assessment service
    • Privacy
      • GDPR
      • CCPA/CPRA
    • Additional Services
      • International Services 
      • Multi-Framework 
      • AS9100
      • Microsoft SSPA
      • NIS2
      • C5
      • SOX 404
      • CSA STAR
      • Business Continuity & Disaster Recovery
      • Limited Access Death Master File
    • All Services
  • Platform
  • Company
    • About Us
    • Partners
    • Meet our team
    • Board of Directors
    • Careers
    • Community
  • Customers
  • Resources
    • Resource Center
    • Blogs
    • Case Studies 
    • Videos 
    • Events
    • By Service
      • SOC 2 
      • ISO 27001 
      • ISO 42001 
      • CMMC
      • FedRAMP
      • HITRUST
      • PenTest 
  • A-SCEND Login
  • Careers
CONTACT US