GovRAMP Assessment | A-LIGN
  • Services
        • SOC Assessments 

        • SOC 1
        • SOC 2
        • ISO Certifications 

        • ISO 27001
        • ISO 27701
        • ISO 22301
        • ISO 42001
        • ISO 45001 
        • ISO 14001
        • ISO 9001
        • Government Assessments 

        • All Government
        • FedRAMP
        • GovRAMP
        • IRAP
        • FISMA
        • CMMC
        • NIST 800-171
        • Healthcare Assessments 

        • All Healthcare
        • HITRUST
        • HIPAA
        • Cybersecurity 

        • Penetration testing
        • Red team services
        • Ransomware preparedness assessment
        • Social engineering
        • Vulnerability assessment service
        • Privacy 

        • GDPR
        • CCPA/CPRA
        • PCI Assessments 

        • PCI DSS
        • PCI SSF
        • Additional Services 

        • International Services
        • Multi-Framework
        • AI Governance
        • AIUC-1
        • AS9100
        • Microsoft SSPA
        • NIS2
        • C5
        • SOX 404
        • CSA STAR
        • Business Continuity & Disaster Recovery
        • Limited Access Death Master File
        • All Services
  • Platform
  • Company
        • About Us
        • Partners
        • Meet our team
        • Board of Directors
        • Careers
        • Community
        • image

          TAMPA, Fla. – (Sept 1, 2026) – A-LIGN, the leading cybersecurity compliance company, today announced…

          Learn more
  • Customers
  • Resources
        • Quick links

        • Resource Center
        • Blogs
        • Case Studies 
        • Videos
        • Events
        • By service

        • SOC 2 
        • ISO 27001 
        • ISO 42001 
        • CMMC
        • FedRAMP
        • HITRUST 
        • PenTest
        • Featured Resources

          image
          image
          image
          image
  • A-SCEND Login
  • Careers
CONTACT US
image govramp hero 6 1

GovRAMP Assessment by A-LIGN

Unlock state and local contracts with GovRAMP

A-LIGN is a registered GovRAMP assessor and a FedRAMP-recognized independent assessor. You can consolidate GovRAMP and FedRAMP scoping, evidence, and timelines with one firm. GovRAMP named A-LIGN its first Champion member in October 2024. Win more business with GovRAMP Ready status and GovRAMP Authorized status.

Talk to an expert
image govramp hero 6 1
federal assessments completed

1k+

client satisfaction rating

96%

FedRAMP assessor

Top 3

federal clients served

250+

What is GovRAMP?

A GovRAMP assessment is the independent security evaluation that determines whether a cloud product meets the GovRAMP control baseline, so it can be listed on the GovRAMP marketplace and sold to state, local, and education (SLED) agencies. GovRAMP is the program formerly known as StateRAMP, and its baselines are anchored to NIST 800-53.

The assessment is performed by a registered third-party assessment organization and leads to GovRAMP Ready or GovRAMP Authorized status. A-LIGN is a registered GovRAMP assessor and a FedRAMP 3PAO.

Why A-lign

Win SLED business with GovRAMP authorization

Gain GovRAMP-authorized status from an assessor that has been with the program since its early years. GovRAMP named A-LIGN its first Champion member in October 2024, and A-LIGN was among the first assessors to register with the program. A-LIGN is a registered GovRAMP assessor and one of the top three FedRAMP assessors in the world, with the credentials to validate your GovRAMP impact level and assess your environment against the relevant NIST 800-53 Rev. 5 and GovRAMP controls.

Get started
image govamp a scend 6 0

Win business with state and local governments

GovRAMP Authorization opens the door to contracts with state and local government agencies. SLED buyers increasingly require an independent security validation before they will purchase or renew a cloud product, and GovRAMP is the standardized framework state and local procurement teams now look for. Without an authorization on the GovRAMP marketplace, your offering competes on assertions. With one, you compete on a recognized, third-party-validated status that procurement officers can trust at face value.

Prove you meet state cloud security requirements

A GovRAMP Ready or GovRAMP Authorized status proves your cloud product meets the security requirements states have adopted for the data they hold. The assessment validates your environment against NIST 800-53 Rev. 5 controls and the GovRAMP-specific control baseline for your impact level.

That validated status is what tells a SLED buyer your environment is fit to handle their information, before procurement asks the question.

One assessment, many state requirements

A single GovRAMP assessment satisfies multiple state requirements at once. Instead of responding to a different security questionnaire or attestation for every state contract, your authorization on the GovRAMP marketplace covers participating states and entities under one common framework.

That is a faster path to revenue across the SLED market and a lower compliance cost than maintaining a per-state response motion.

OUR SERVICES

Your path from GovRAMP Ready to Authorized

A-LIGN supports every step of your GovRAMP journey, from an initial readiness review through the full security assessment that earns your place on the GovRAMP marketplace. And because the same federal practice delivers FedRAMP, NIST 800-171, and FISMA assessments, you can consolidate scoping, evidence, and timelines under a single assessor.

Contact us

GovRAMP Readiness Assessment Report (RAR)

We review your environment and determine if it is technically capable of meeting the GovRAMP requirements for an official Ready status on the GovRAMP marketplace.

GovRAMP pre-assessment

Prior to beginning the security assessment, we assess your environment to identify potential non-conformities and benchmark against GovRAMP requirements so you can address known issues before the official assessment.

GovRAMP assessment

As a GovRAMP registered assessor and a FedRAMP-recognized independent assessor (formerly 3PAO), we validate your GovRAMP impact level and assess compliance with the relevant controls defined in NIST 800-53 Rev. 5 and by GovRAMP, including interviews, examination, and testing.

FedRAMP

A-LIGN is a top three FedRAMP assessor with 1,000+ federal assessments completed. The same federal practice that runs your GovRAMP work can take you all the way to FedRAMP authorization.

Learn more

NIST 800-171

NIST 800-171 governs the protection of controlled unclassified information (CUI) in non-federal systems and is a common parallel obligation for SLED suppliers. A-LIGN runs the assessment alongside your GovRAMP and FedRAMP work.

Learn more

FISMA

FISMA establishes the federal information security baseline for systems operated by or on behalf of federal agencies. A-LIGN’s federal practice supports FISMA assessments under the same NIST 800-53 control set that anchors GovRAMP.

Learn more
Service Grid side image 6 0

A-LIGN by the numbers

audits completed
36k+
customer satisfaction
96%
clients globally
6.4k+
auditors globally
400+
Platform Innovation

Modernized compliance makes rigor repeatable

A-SCEND combines human expertise and robust processes with powerful technology to help you achieve compliance, grow your business, and expand into new markets without sacrificing rigor.

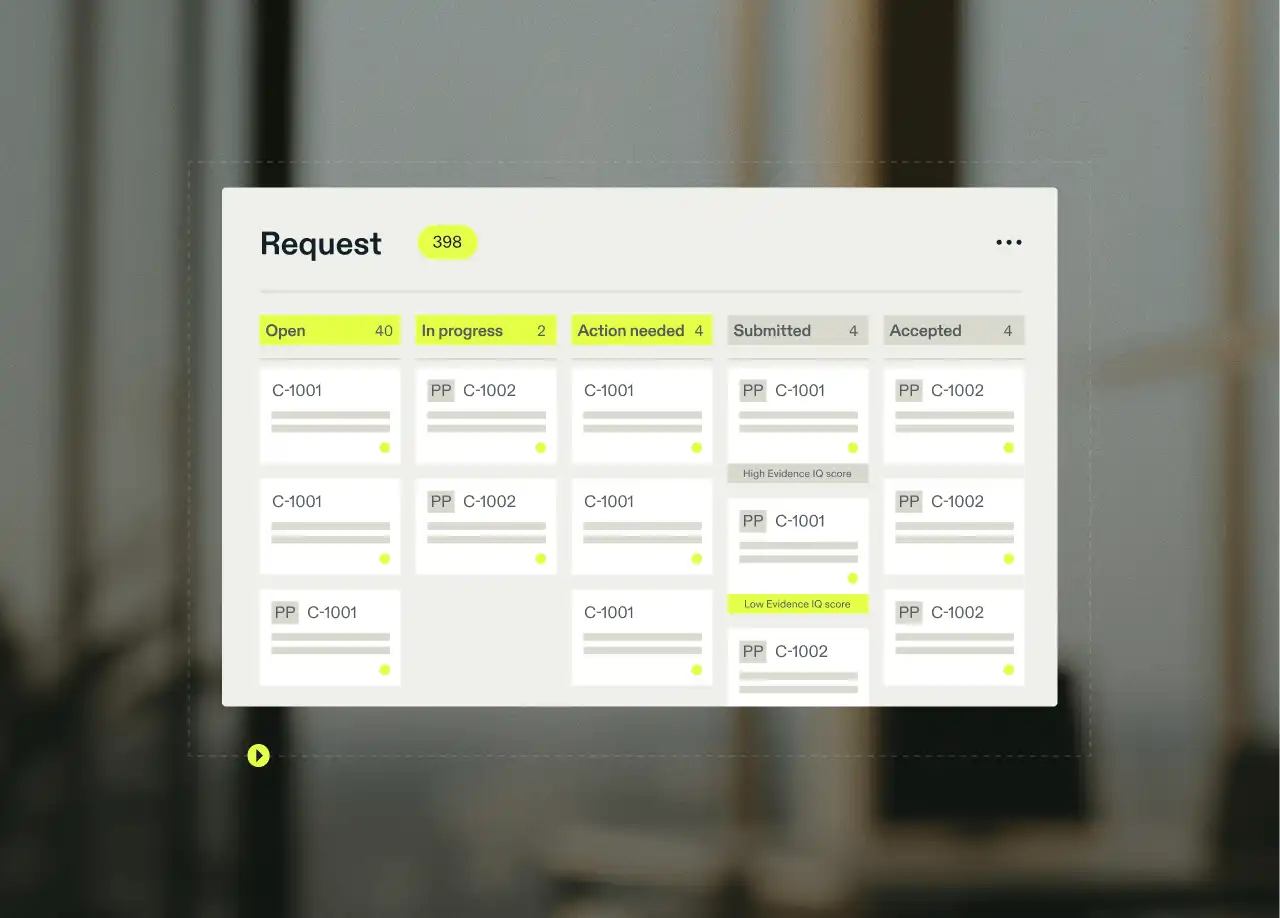
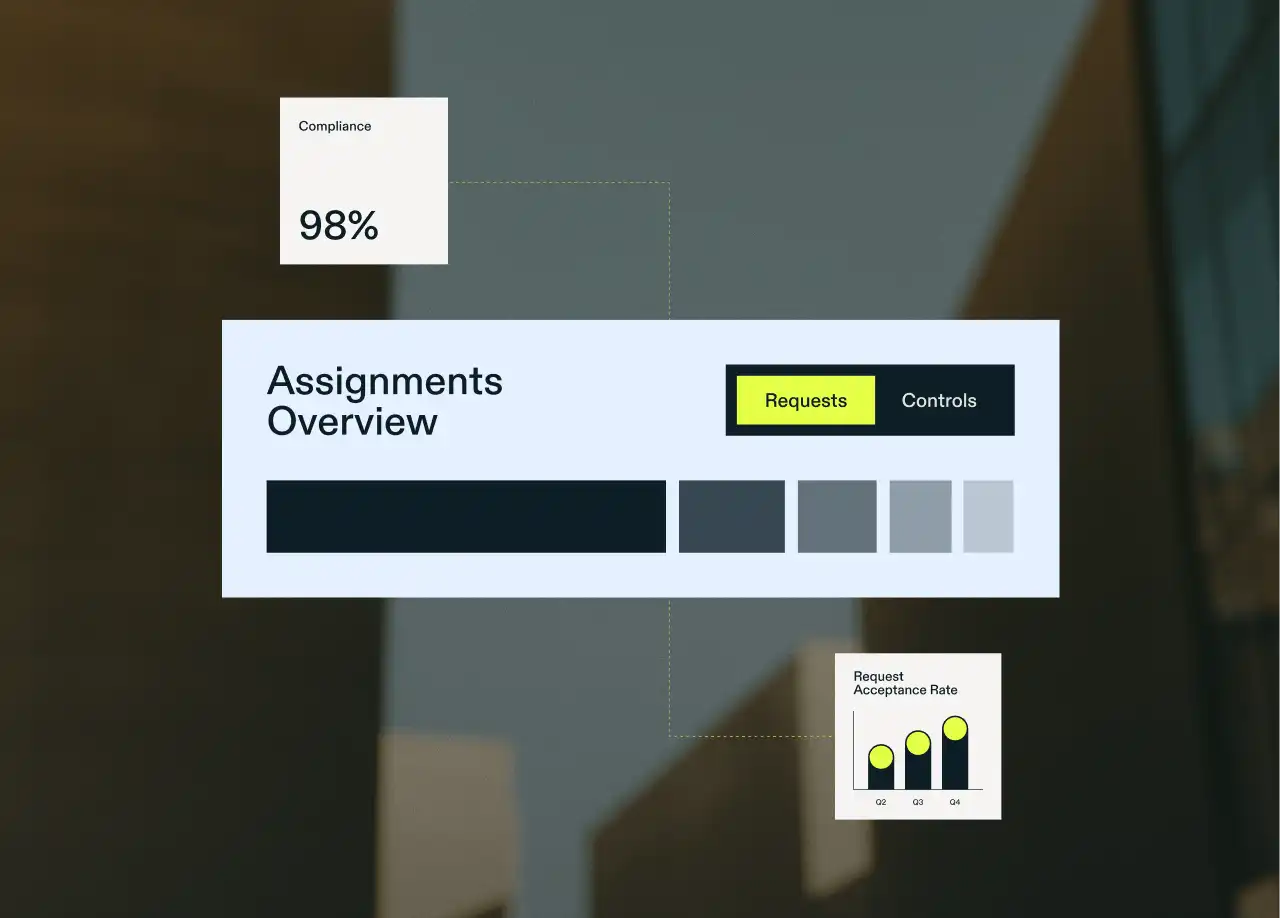
A-SCEND platform showing centralized audit requests
A-SCEND platform showing the guided audit workflow stages
EFFICIENT AUDIT PLATFORM

Tech-enabled audit management

A-SCEND is an end-to-end audit management platform built from real-world audit practice. By eliminating repetitive tasks, delivering real-time visibility and control, and enforcing consistency and precision across every engagement, A-SCEND elevates audit quality without sacrificing rigor.

Purpose-built technology enforces consistency, strengthens audit quality, and drives efficiency, every cycle, every framework, every year.

RIGOROUS METHODOLOGY 

Precision at every stage

Every A-SCEND engagement follows a disciplined methodology built to withstand scrutiny.

That rigor carries through every stage of our audit process, from precise scoping and a deep understanding of your business up front, with executive oversight and built-in quality checks, to expert review and fine-tuning for a polished, high-quality report.

That experience and discipline bring greater certainty and help prevent the leading causes of report rejection: incomplete scope and missing controls.
SUCCESS STORIES

Why security leaders trust A-LIGN

“I would like to thank A-LIGN and their staff for the great service A-LIGN has provided KeyPoint on our recent FISMA audits. A-LIGN has been truly a great partner with the flexibility of getting staff on-site to meet our customer requirements.”

KeyPoint (now Peraton)

client testimonial Peraton

“RegScale operates in highly regulated environments where trust and compliance are non-negotiable. That’s why we chose A-LIGN — experts with deep federal compliance expertise across the full spectrum of frameworks — to serve as our trusted audit partner.”

Learn more

CISO

Dale Hoak

RegScale

RegScale logo

“We needed more than just an auditor. We needed a strategic partner who could help us achieve our current and future federal compliance goals. We found a true partner in A-LIGN.”

Learn more

Senior Compliance Manager

Micah Hedges

Island

client testimonial island

“We appreciate the support and communication from the A-LIGN team, from the audit staff to the account managers who take the time to understand our needs and objectives. With A-LIGN, it feels more like a partnership than an assigned number or contract."

Manager Digital Trust

Christopher Sharples

Dig Insights

Dig Insights logo
Helpful Resources

Support for your compliance journey

From guides to whitepapers, we’ve got the resources to move your compliance program forward.

View resources
Resource Article A LIGN Releases 2026 Compliance Benchmark Report 1 0
BLOG
A-LIGN Releases 2026 Compliance Benchmark Report
Learn more
Resource Webinar FedRAMP 20x Unlocking New Opportunities 1 0
Video
FedRAMP 20x: Unlocking New Opportunities
Learn more
Resource Article The FedRAMP 2026 Consolidated Rules 1 0
Blog
The FedRAMP 2026 Consolidated Rules: What Cloud Service Providers Need to Know
Learn more
resource Mostly Compliant Ep14 1 0
Video
AI, FedRAMP, and the Future of Federal Compliance w/ Jacob Hill
Learn more

Frequently asked questions

Contact us

Is GovRAMP the same thing as StateRAMP?

GovRAMP is the program formerly known as StateRAMP. Same marketplace, same control baselines anchored to NIST 800-53, same authorization model for cloud products serving state, local, and education buyers. If a procurement document, RFP, or partner still says “StateRAMP,” your GovRAMP Ready or GovRAMP Authorized status is what they are asking for.

We are pursuing FedRAMP. Do we still need GovRAMP for state contracts?

FedRAMP authorization does not automatically satisfy state procurement requirements, even though both rely on NIST 800-53. State and local agencies are increasingly asking for a GovRAMP marketplace listing as the standardized signal that your environment is fit for SLED data, and a separate GovRAMP assessment puts you on that marketplace. The work overlaps heavily, which is why running GovRAMP and FedRAMP with the same assessor consolidates evidence, scoping, and timeline rather than duplicating them.

Can we reuse evidence from SOC 2, ISO 27001, or an existing FedRAMP package for GovRAMP?

Much of it, yes. Controls evidence collected under SOC 2 Type II, ISO 27001, or a FedRAMP authorization maps directly to the GovRAMP control baseline, so an experienced assessor scopes the engagement around the gap rather than starting from scratch. The savings are real on the Moderate and High paths, where the NIST 800-53 control overlap with FedRAMP is substantial.

Which GovRAMP Impact level do we actually need?

The sensitivity of the data your cloud product handles for SLED customers sets your Impact level. Company size and revenue do not factor in. GovRAMP names four levels. Low covers publicly available, non-sensitive data. Low+ adds selected Moderate controls for limited sensitive data. Moderate aligns to the FedRAMP Moderate control baseline and is the level most state agencies buy for. High covers the most sensitive workloads and became a full GovRAMP impact level in 2026. Getting the level right at scoping is what determines the assessment’s cost, timeline, and addressable market.

What is the difference between GovRAMP Ready and GovRAMP Authorized?

GovRAMP Ready means an independent assessor has reviewed your security documentation and confirmed your cloud product is on a credible path to authorization. It is recorded on the GovRAMP marketplace as a progress status and signals to SLED buyers that your environment has been independently reviewed, but it is not an authorization.

GovRAMP Authorized means the full assessment is complete, the control baseline has been tested, and a GovRAMP Approvals Committee or a sponsoring state agency has granted authorization.

Ready is achievable in a fraction of the time and is often enough to stay in an active procurement while the full assessment runs.

What is a GovRAMP Readiness Assessment Report (RAR)?

The Readiness Assessment Report is the deliverable an assessor produces when evaluating whether your cloud product is prepared for a full GovRAMP assessment. It documents your system boundary, the control implementations already in place, and the gaps that need remediation before the formal assessment begins. A completed RAR is what earns GovRAMP Ready status on the marketplace.

Organizations that arrive at the full assessment with a remediated RAR consistently spend less on the assessment itself, because the assessor is testing controls rather than resolving documentation deficiencies.

How long does a GovRAMP assessment take?

Timeline depends on Impact level, the maturity of your existing documentation, and whether you hold a relevant certification already. Organizations coming in with a current SOC 2 Type II, ISO 27001, or FedRAMP package move substantially faster, because much of the evidence maps directly to the GovRAMP baseline.

The readiness phase is usually the longest stage; the assessment itself is measured in weeks once the system boundary is settled and evidence is in place. A-LIGN scopes the engagement around the gap between what you already hold and what GovRAMP requires, then gives you a milestone plan before work begins.

How much does a GovRAMP assessment cost?

GovRAMP assessment cost is driven by Impact level, the size and complexity of your system boundary, and how much of the control baseline is already evidenced by an existing certification. Impact I engagements covering low-impact data are materially less expensive than Impact II or III, where the NIST 800-53 baseline is broader.

Organizations pursuing GovRAMP and FedRAMP with the same assessor consolidate scoping, evidence collection, and testing rather than paying for both separately. The assessment fee excludes internal labor, remediation, and tooling. Contact A-LIGN for a scoped estimate based on your Impact level and system boundary.

pre footer cta architecture 005 1 1 scaled

Ready to get started?

Contact us

Sign-up for our newsletter to be the first to know about upcoming events and new content from A-LIGN.

  • Services
  • SOC 1
  • SOC 2
  • ISO 27001
  • ISO 42001
  • FedRAMP
  • CMMC
  • IRAP
  • HITRUST
  • Penetration Testing
  • PCI DSS
  • HIPAA
  • International Services
  • Multi-Framework
  • AI Governance
  • All Services
  • Company 
  • About us
  • Partners
  • Platform
  • Careers
  • Our Team
  • Community
  • Trust Center
  • Contact Us
  • Customers 
  • Customer Stories 
  • Resources
  • Resource Center
  • Blogs
  • Case Studies
  • Videos
  • Events
  • Newsletter Sign-up
  • Guides
  • SOC 2 Compliance
  • ISO 27001 Certification
  • CMMC Compliance
  • ISO 42001 Compliance
  • HITRUST Certification
More
  • ISO Certificate Directory
  • Privacy Policy
  • Cookie Policy
  • Impartiality and Inquiries
  • Acceptable Use Policy
  • Sitemap
  • AI Information

Rigor, made
repeatable.

A-LIGN is the leading cybersecurity compliance partner, trusted by over 6,400 organizations worldwide to navigate the complexities of compliance, audit, and risk. With a tech-enabled delivery model and deep domain expertise, A-LIGN delivers high-quality, efficient audits across frameworks including SOC 2, ISO 27001, FedRAMP, CMMC, ISO 42001, PCI, and HITRUST.

A-LIGN 2026. All rights reserved.

  • Services
    • SOC Assessments
      • SOC 1
      • SOC 2
    • ISO Certifications 
      • ISO 27001
      • ISO 27701
      • ISO 22301
      • ISO 42001
      • ISO 45001 
      • ISO 14001
      • ISO 9001
    • Healthcare Assessments 
      • All Healthcare
      • HITRUST
      • HIPAA
    • Government Assessments
      • All Government
      • FedRAMP
      • GovRAMP
      • IRAP
      • FISMA
      • CMMC
      • NIST 800-171
    • PCI Assessments
      • PCI DSS
      • PCI SSF
    • Cybersecurity
      • Penetration testing
      • Red team services
      • Ransomware preparedness assessment
      • Social engineering
      • Vulnerability assessment service
    • Privacy
      • GDPR
      • CCPA/CPRA
    • Additional Services
      • International Services 
      • Multi-Framework 
      • AS9100
      • Microsoft SSPA
      • NIS2
      • C5
      • SOX 404
      • CSA STAR
      • Business Continuity & Disaster Recovery
      • Limited Access Death Master File
    • All Services
  • Platform
  • Company
    • About Us
    • Partners
    • Meet our team
    • Board of Directors
    • Careers
    • Community
  • Customers
  • Resources
    • Resource Center
    • Blogs
    • Case Studies 
    • Videos 
    • Events
    • By Service
      • SOC 2 
      • ISO 27001 
      • ISO 42001 
      • CMMC
      • FedRAMP
      • HITRUST
      • PenTest 
  • A-SCEND Login
  • Careers
CONTACT US