

CMMC checklist
Your guide to preparing for CMMC certification
The Cybersecurity Maturity Model Certification (CMMC) program was developed by the Department of Defense (DoD) to ensure contractors and subcontractors implement cybersecurity controls and processes that adequately protect Controlled Unclassified Information (CUI) and Federal Contract Information (FCI) residing on Defense Industrial Base (DIB) systems and networks.
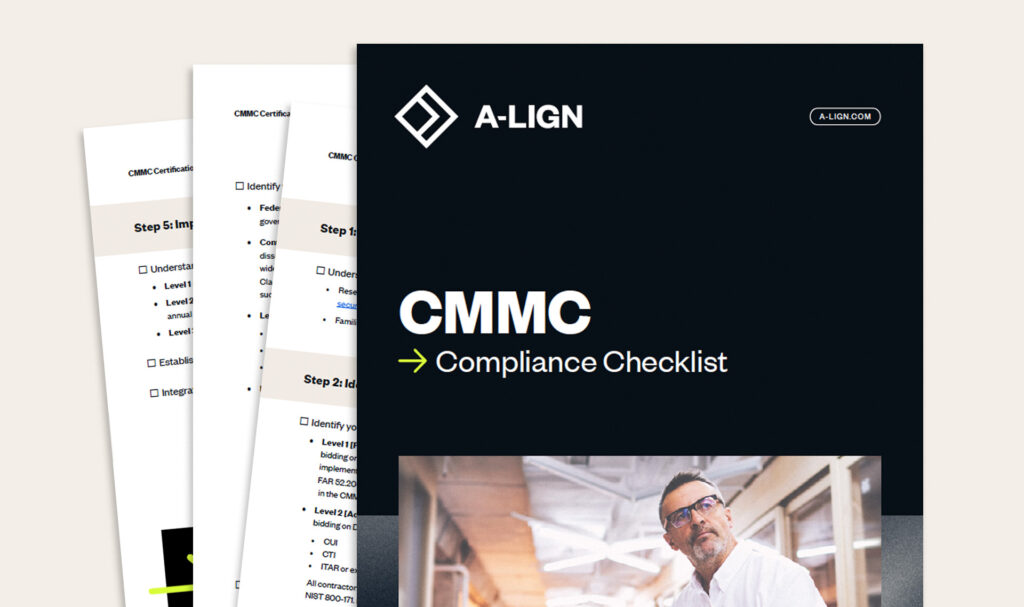
Download your checklist
Download the checklist to learn how to:

Understand CMMC program requirements and NIST 800-171 Rev 2
Identify CMMC level, in-scope assets, and gaps in your compliance program
Prepare an implementation plan, documentation, and for your C3PAO assessment
Choose a C3PAO and undergo the assessment
Continuously improve your CMMC compliance and adhere to future requirements
5,700+ companies trust A-LIGN for their compliance and cybersecurity needs


A top FedRAMP assessor with extensive experience in NIST frameworks
One stop for all your compliance efforts
A-LIGN leverages a vast network of resources, experience, and professional relationships to ensure your organization is ready and approved to support government agencies, minimize risks, and keep their data safe against cybersecurity threats.
FedRAMP
If you are a Cloud Service Provider (CSP) currently providing, or seeking to provide, services to federal agencies, A-LIGN can make your FedRAMP process seamless. We will support you during your entire FedRAMP journey, from readiness to authorization.
FISMA
A-LIGN’s expert federal assessors can help your company meet FISMA’s requirements for all agencies to develop, document, and implement an information security and protection program.
NIST 800-171
As an organization interested in working on a federal contract, you must implement the appropriate NIST 800-171 controls. These cybersecurity control measures protect vital information in nonfederal systems and organizations.


“A-LIGN was a strong partner throughout the process to achieve CMMC Level 2 certification. Their structured approach and expertise helped validate the work our cybersecurity team has done.”
Cory Wilson, Director of Information Technology at Quiet Professionals
Get your guide to CMMC certification
From readiness to certification, A-LIGN has everything you need to work with the Department of Defense. Download our checklist to help your organization prepare to achieve certification success.
