IRAP Assessment
  • Services
        • SOC Assessments 

        • SOC 1
        • SOC 2
        • ISO Certifications 

        • ISO 27001
        • ISO 27701
        • ISO 22301
        • ISO 42001
        • ISO 45001 
        • ISO 14001
        • ISO 9001
        • Federal Assessments 

        • All Government
        • FedRAMP
        • GovRAMP
        • FISMA
        • CMMC
        • NIST 800-171
        • Healthcare Assessments 

        • All Healthcare
        • HITRUST
        • HIPAA
        • Cybersecurity 

        • Penetration testing
        • Red team services
        • Ransomware preparedness assessment
        • Social engineering
        • Vulnerability assessment service
        • Privacy 

        • GDPR
        • CCPA/CPRA
        • PCI Assessments 

        • PCI DSS
        • PCI SSF
        • Additional Services 

        • International Services
        • Multi-Framework
        • AI Governance
        • AIUC-1
        • AS9100
        • Microsoft SSPA
        • NIS2
        • C5
        • SOX 404
        • CSA STAR
        • Business Continuity & Disaster Recovery
        • Limited Access Death Master File
        • All Services
  • Platform
  • Company
        • About Us
        • Partners
        • Meet our team
        • Board of Directors
        • Careers
        • Community
        • image

          Veteran-owned elite cybersecurity team expands A-LIGN’s ability to help organizations move beyond compliance and stay…

          Learn more
  • Customers
  • Resources
        • Quick links

        • Resource Center
        • Blogs
        • Case Studies 
        • Videos
        • Events
        • By service

        • SOC 2 
        • ISO 27001 
        • ISO 42001 
        • CMMC
        • FedRAMP
        • HITRUST 
        • PenTest
        • Featured Resources

          image
          image
          image
          image
  • A-SCEND Login
  • Careers
CONTACT US
image service IRAP hero 6 0

IRAP Assessment

Your gateway to the Australian government market

IRAP has shifted from a competitive advantage to a strict baseline requirement for doing business with Australia’s public sector. A-LIGN brings local IRAP expertise and Australian delivery resources under the same roof as your SOC 2 and ISO 27001 program, one partner, every framework Australia requires.

Talk to an expert
image service IRAP hero 6 0
Why A-lign

One partner for IRAP, SOC 2, and ISO 27001

IRAP is an independent assessment of your security controls against the Australian Government's Information Security Manual (ISM). It's now a mandate for cloud service providers and a critical requirement for any company pursuing government or municipal contracts in Australia, one of the most tightly regulated markets in the Asia-Pacific region.

Get started
image IRAP a scend 6 0 (1)

Local expertise, global standards

Australian-based practitioners leverage A-LIGN's audit methodology, sharpened across 36,000+ engagements worldwide, giving you local credibility backed by global rigor.

Compliance as a growth driver

As you expand across Australia and the broader APAC region, A-LIGN's depth across frameworks scales with you. IRAP's control set overlaps with ISO 27001 and SOC 2. A-SCEND maps shared requirements so your evidence does more than one job.

Align with government expectations

IRAP is crucial for organizations aiming to work with Australian government agencies. It signals a commitment to protecting sensitive data and complying with regulatory frameworks.

OUR SERVICES

IRAP services for every stage

A-LIGN's IRAP assessments are delivered by ASD-endorsed assessors against the Australian Government Information Security Manual (ISM) and Protective Security Policy Framework (PSPF), so your report holds up to government and enterprise scrutiny.

Contact us

IRAP Readiness Assessment

Evaluates your controls against the ISM before the formal assessment begins, surfacing gaps while there’s still time to fix them.

IRAP Security Assessment

An independent, ASD-aligned assessment of your system’s security controls, covering classifications up to SECRET.

Security Assessment Report & SCM

A four-stage delivery: plan and prepare, define scope, assess controls, and produce your report and security controls matrix.

Reassessment & Ongoing Compliance

PSPF requirement 0109 expects a current IRAP assessment within the prior 24 months. We help you stay ahead of the renewal window.

Service Grid side image 6 0

A-LIGN by the numbers

audits completed
36k+
customer satisfaction
96%
clients globally
6.4k+
auditors globally
400+
Platform Innovation

Modernized compliance makes rigor repeatable

A-SCEND combines human expertise and robust processes with powerful technology to help you achieve compliance, grow your business, and expand into new markets without sacrificing rigor.

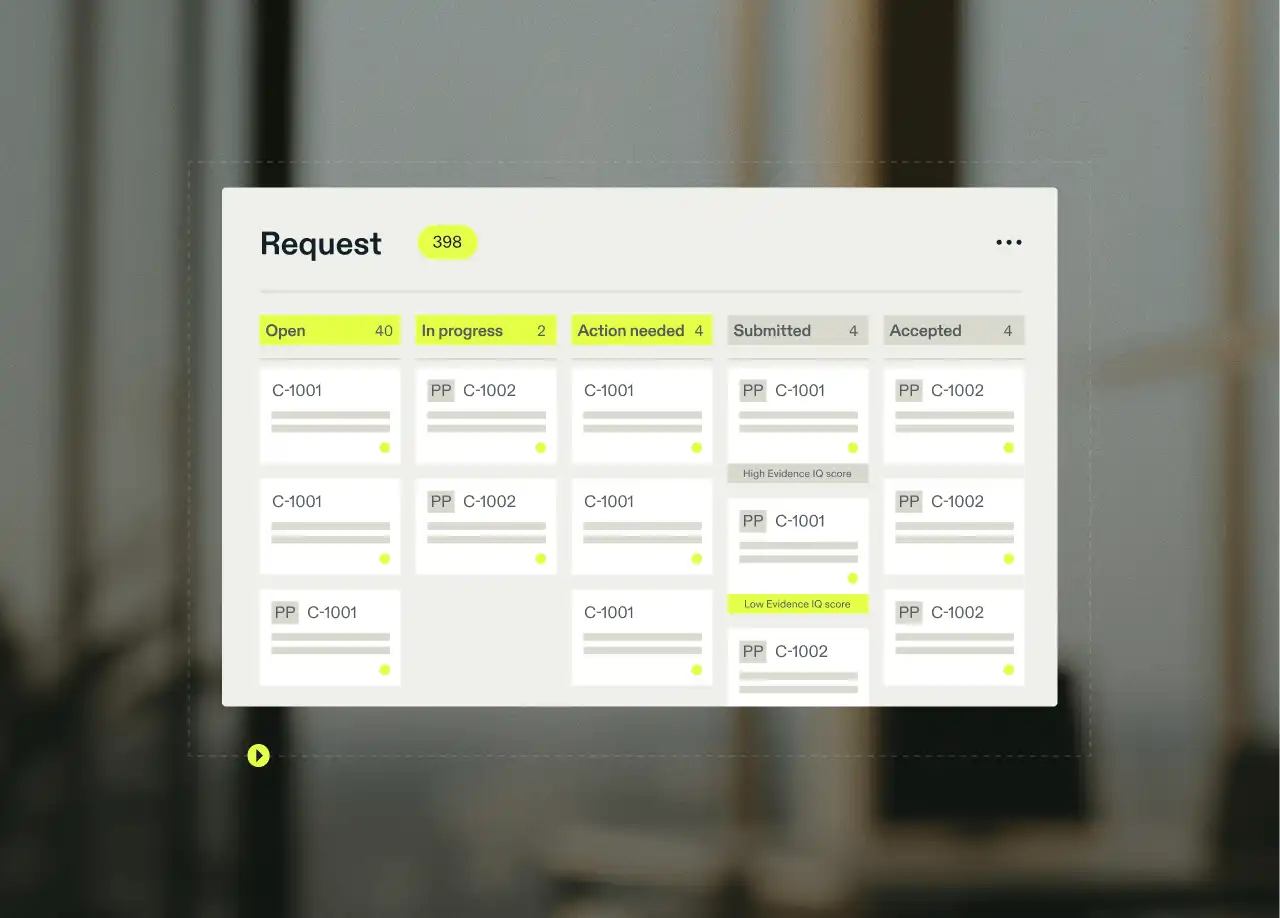
A-SCEND platform showing centralized audit requests
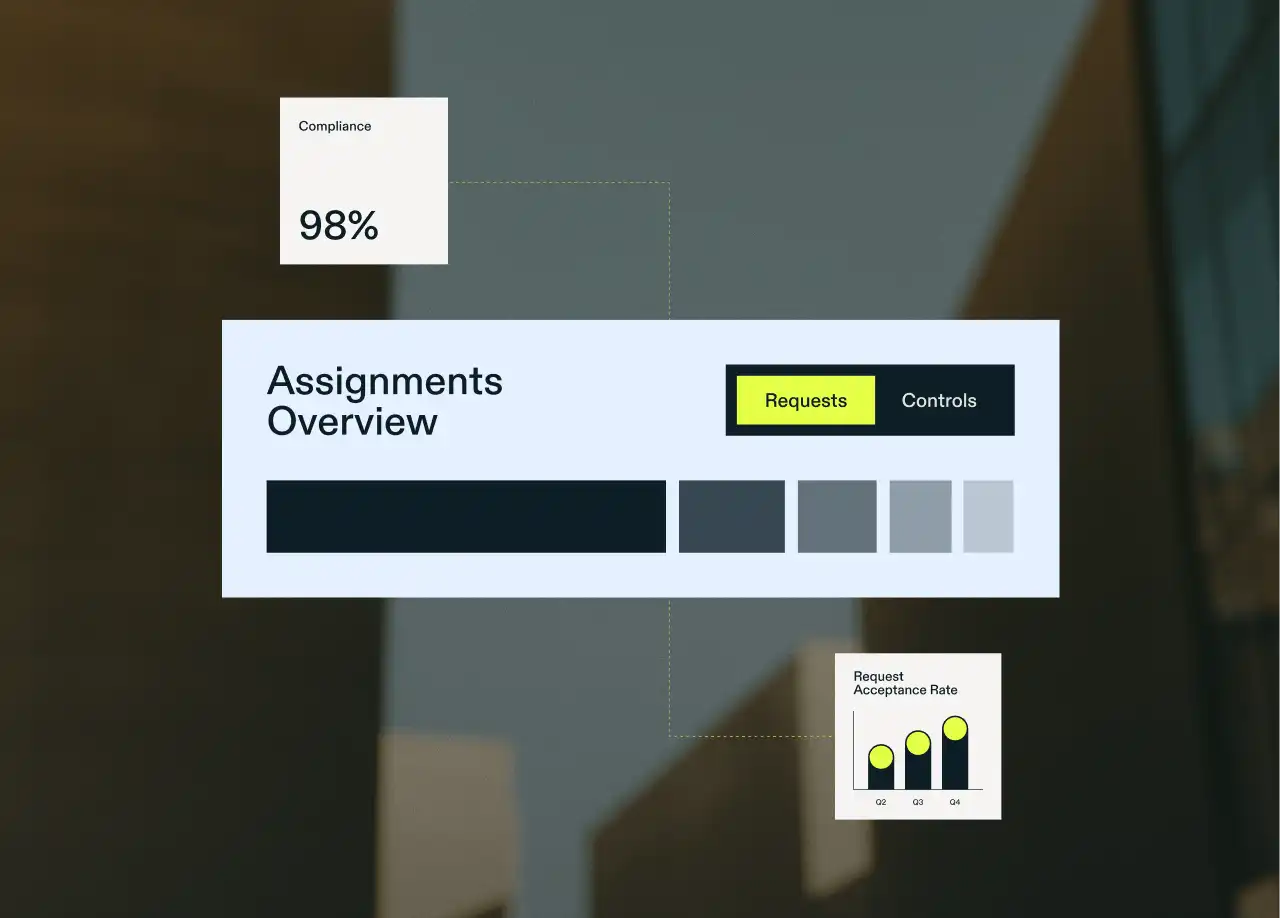
A-SCEND platform showing the guided audit workflow stages
EFFICIENT AUDIT PLATFORM

Tech-enabled audit management

A-SCEND is an end-to-end audit management platform built from real-world audit practice. By eliminating repetitive tasks, delivering real-time visibility and control, and enforcing consistency and precision across every engagement, A-SCEND elevates audit quality without sacrificing rigor.

Purpose-built technology enforces consistency, strengthens audit quality, and drives efficiency, every cycle, every framework, every year.

RIGOROUS METHODOLOGY 

Precision at every stage

Every A-SCEND engagement follows a disciplined methodology built to withstand scrutiny.

That rigor carries through every stage of our audit process, from precise scoping and a deep understanding of your business up front, with executive oversight and built-in quality checks, to expert review and fine-tuning for a polished, high-quality report.

That experience and discipline bring greater certainty and help prevent the leading causes of report rejection: incomplete scope and missing controls.
Helpful Resources

Support for your compliance journey

From guides to whitepapers, we've got the resources to move your compliance program forward.

View resources
Whitepaper
2026 Compliance Benchmark Report
Learn more
resource Video ISO 42001 virtual workshop 1 0
Video
ISO 42001 Virtual Workshop: From AI Adoption to AI Assurance
Learn more
Blog
SOC 2 Checklist: Preparing for a SOC 2 Audit 
Learn more
Resource SAS 6 0
Case Study
SAS improves audit harmonization and efficiency with A-LIGN
Learn more

Frequently asked questions

Contact us

What is IRAP and why does it matter?

IRAP (Information Security Registered Assessors Program) is an Australian Signals Directorate initiative that provides independent assessment of an organization's security controls against the Australian Government's Information Security Manual (ISM). It has become mandatory for cloud service providers and a critical requirement for companies pursuing government and municipal contracts in Australia.

Who needs an IRAP assessment?

Cloud and SaaS providers hosting government workloads, and any vendor bidding on Australian federal, state, or local government contracts. The trigger is the buyer and the data involved, not company size — a small SaaS vendor handling government data carries the same obligation as a hyperscaler.

Do we need IRAP if we already have SOC 2 or ISO 27001?

Likely yes, if you're pursuing Australian government business — IRAP is assessed against the ISM specifically, which Australian agencies require regardless of other certifications. The good news: IRAP's control set overlaps substantially with SOC 2 and ISO 27001, so much of your existing evidence can be reused rather than rebuilt.

How long does an assessment take, and how often do we need to reassess?

Timelines vary with scope, but assessments follow four stages: plan and prepare, define scope, assess controls, and produce the report and security controls matrix. Under PSPF requirement 0109, agencies expect a current IRAP assessment completed within the prior 24 months, so reassessment is a recurring part of maintaining eligibility.

Does A-LIGN have assessors based in Australia?

Yes. Through our acquisition of AssurePoint, A-LIGN now has local, ASD-endorsed IRAP practitioners and delivery resources based in Australia, combined with A-LIGN's global audit methodology.

pre footer cta architecture 005 1 1 scaled

Ready to get started?

Contact us

A-LIGN is the leading cybersecurity compliance partner, trusted by over 6,400 organizations worldwide to navigate the complexities of compliance, audit, and risk. With a tech-enabled delivery model and deep domain expertise, A-LIGN delivers high-quality, efficient audits across frameworks including SOC 2, ISO 27001, FedRAMP, CMMC, ISO 42001, PCI, and HITRUST.

CONTACT US
  • Services
  • SOC 1
  • SOC 2
  • ISO 27001
  • ISO 42001
  • CMMC
  • HITRUST
  • FedRAMP
  • Penetration Testing
  • PCI DSS
  • HIPAA
  • International Services
  • Multi-Framework
  • AI Governance
  • All Services
  • Company 
  • About us
  • Partners
  • Platform
  • Careers
  • Our Team
  • Community
  • Trust Center
  • Contact Us
  • Customers 
  • Customer Stories 
  • Resources
  • Resource Center
  • Blogs
  • Case Studies
  • Videos
  • Events
  • Newsletter Sign-up
  • Guides
  • SOC 2 Compliance
  • ISO 27001 Certification
  • CMMC Compliance
  • ISO 42001 Compliance
  • HITRUST Certification
  • ISO Certificate Directory
  • Privacy Policy
  • Cookie Policy
  • Impartiality and Inquiries
  • Acceptable Use Policy
  • Sitemap
  • AI Information

Price and Associates CPAs, LLC dba A-LIGN ASSURANCE is a licensed certified public accounting firm registered with the Public Company Accounting Oversight Board (PCAOB). A-LIGN Compliance and Security, Inc. dba A-LIGN is a leading cybersecurity and compliance professional services firm.

A-LIGN 2026. All rights reserved.

  • Services
    • SOC Assessments
      • SOC 1
      • SOC 2
    • ISO Certifications 
      • ISO 27001
      • ISO 27701
      • ISO 22301
      • ISO 42001
      • ISO 45001 
      • ISO 14001
      • ISO 9001
    • Healthcare Assessments 
      • All Healthcare
      • HITRUST
      • HIPAA
    • Federal Assessments
      • All Government
      • FedRAMP
      • StateRAMP
      • FISMA
      • CMMC
      • NIST 800-171
    • PCI Assessments
      • PCI DSS
      • PCI SSF
    • Cybersecurity
      • Penetration testing
      • Red team services
      • Ransomware preparedness assessment
      • Social engineering
      • Vulnerability assessment service
    • Privacy
      • GDPR
      • CCPA/CPRA
    • Additional Services
      • International Services 
      • Multi-Framework 
      • AS9100
      • Microsoft SSPA
      • NIS2
      • C5
      • SOX 404
      • CSA STAR
      • Business Continuity & Disaster Recovery
      • Limited Access Death Master File
    • All Services
  • Platform
  • Company
    • About Us
    • Partners
    • Meet our team
    • Board of Directors
    • Careers
    • Community
  • Customers
  • Resources
    • Resource Center
    • Blogs
    • Case Studies 
    • Videos 
    • Events
    • By Service
      • SOC 2 
      • ISO 27001 
      • ISO 42001 
      • CMMC
      • FedRAMP
      • HITRUST
      • PenTest 
  • A-SCEND Login
  • Careers
CONTACT US